Showing posts with label Login. Show all posts

Thursday, 27 September 2012

Spring MVC Customized User Login Logout Implementation Example

This post describes how to  implement a customized user access to an Spring MVC web application (login logout). As a prerequisite, readers are advised to read this post which introduces several Spring Security concepts.

The code example is available from Github in the Spring-MVC-Login-Logout directory. It is derived from the Spring MVC with annotations example.

Customized Authentication Provider

In order to implement our own way of accepting user login requests, we need to implement an authentication provider. The following lets users in if their id is identical to their passwords:
public class MyAuthenticationProvider implements AuthenticationProvider {

    private static final List<GrantedAuthority> AUTHORITIES
        = new ArrayList<GrantedAuthority>();

    static {
        AUTHORITIES.add(new SimpleGrantedAuthority("ROLE_USER"));
        AUTHORITIES.add(new SimpleGrantedAuthority("ROLE_ANONYMOUS"));
    }

    @Override
    public Authentication authenticate(Authentication auth)
        throws AuthenticationException {

        if (auth.getName().equals(auth.getCredentials())) {
            return new UsernamePasswordAuthenticationToken(auth.getName(),
                auth.getCredentials(), AUTHORITIES);
        }

        throw new BadCredentialsException("Bad Credentials");

    }

    @Override
    public boolean supports(Class<?> authentication) {
        
        if ( authentication == null ) return false;

        return Authentication.class.isAssignableFrom(authentication);
    }

}

Security.xml

We need to create a security.xml file:
<beans:beans xmlns="http://www.springframework.org/schema/security"
  xmlns:beans="http://www.springframework.org/schema/beans"
  xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
  xsi:schemaLocation="http://www.springframework.org/schema/beans
    http://www.springframework.org/schema/beans/spring-beans-3.0.xsd
    http://www.springframework.org/schema/security
    http://www.springframework.org/schema/security/spring-security-3.1.xsd">

    <http>
        <intercept-url pattern="/*" access="ROLE_ANONYMOUS"/>
        <form-login
            default-target-url="/"
            always-use-default-target="true" />
        <anonymous />
        <logout />
    </http>

    <authentication-manager alias="authenticationManager">
      <authentication-provider ref="myAuthenticationProvider" />
    </authentication-manager>

    <beans:bean id="myAuthenticationProvider"
      class="com.jverstry.LoginLogout.Authentication.MyAuthenticationProvider" />
    </beans:beans>
The above makes sure all users have the anonymous role to access any page. Once logged in, they are redirected to the main page. If they don't log in, they are automatically considered as anonymous users. A logout function is also declared. Rather than re-implementing the wheel, we use items delivered by Spring itself.

Main Page

We implement a main page displaying the name of the currently logged in user, together with login and logout links:
<%@ taglib prefix="c" uri="http://java.sun.com/jsp/jstl/core" %>
<!doctype html>
<html lang="en">
<head>
  <meta charset="utf-8">
  <title>Welcome To MVC Customized Login Logout!!!</title>
</head>
  <body>
    <h1>Spring MVC Customized Login Logout !!!</h1>
    Who is currently logged in? <c:out value="${CurrPrincipal}" /> !<br />
    <a href="<c:url value='/spring_security_login'/>">Login</a>&nbsp;
    <a href="<c:url value='/j_spring_security_logout'/>">Logout</a>
  </body>
</html>

Controller

We need to provide the currently logged in user name to the view:
@Controller
public class MyController {

    @RequestMapping(value = "/")
    public String home(Model model) {

        model.addAttribute("CurrPrincipal",
            SecurityContextHolder.getContext()
                .getAuthentication().getName());

        return "index";

    }

}

Running The Example

Once compiled, one can start the example by browsing: http://localhost:9292/spring-mvc-login-logout/. It will display the following:
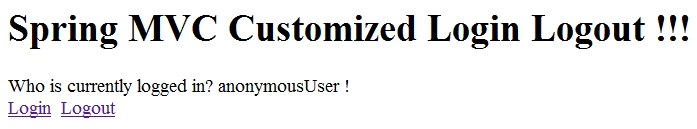
Srping Customized Login Logout

Log in using the same id and password:


The application returns to the main and displays:


More Spring related posts here.

Monday, 17 September 2012

Spring Security And Annotation Configuration Example

This post is the mix between the Spring MVC with Annotations Example and the Spring Security Configuration Introduction. The code example is available on Github in the Spring-Security-And-Annotation-Config directory.

We are going to add a mandatory login page before one can access the main page of the Spring MVC with Annotations example.

Configuration

First, we create a MyServlet-security.xml file:
<beans:beans xmlns="http://www.springframework.org/schema/security"
  xmlns:beans="http://www.springframework.org/schema/beans"
  xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
  xsi:schemaLocation="http://www.springframework.org/schema/beans
    http://www.springframework.org/schema/beans/spring-beans-3.0.xsd

    http://www.springframework.org/schema/security

    http://www.springframework.org/schema/security/spring-security-3.1.xsd">

  <http auto-config="true">
    <intercept-url pattern="/*" access="ROLE_USER"/>
  </http>

  <authentication-manager alias="authenticationManager">
    <authentication-provider>
      <user-service>
        <user authorities="ROLE_USER" name="guest" password="guest"/>
      </user-service>
    </authentication-provider>
  </authentication-manager>

</beans:beans>
We rely on the automatic configuration of Spring security, and we request that one must login with ROLE_USER privilege to access any to page of the website. We set an authentication manager and create a simple guest user login, with the guest password.

We add the security filters under contextConfigLocation:
<?xml version="1.0" encoding="UTF-8"?>
<web-app version="2.5" xmlns="http://java.sun.com/xml/ns/javaee"
  xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
  xsi:schemaLocation="http://java.sun.com/xml/ns/javaee
    http://java.sun.com/xml/ns/javaee/web-app_2_5.xsd">

  <context-param>
    <param-name>contextClass</param-name>
    <param-value>org.springframework.web.context.support.AnnotationConfigWebApplicationContext</param-value>
  </context-param>

  <context-param>
    <param-name>contextConfigLocation</param-name>
    <param-value>
      com.jverstry.Configuration
    </param-value>
  </context-param>

  <filter>
    <filter-name>springSecurityFilterChain</filter-name>
    <filter-class>
      org.springframework.web.filter.DelegatingFilterProxy
    </filter-class>
  </filter>

  <filter-mapping>
    <filter-name>springSecurityFilterChain</filter-name>
    <url-pattern>/*</url-pattern>
  </filter-mapping>

  <listener>
    <listener-class>org.springframework.web.context.ContextLoaderListener</listener-class>
  </listener>

  <servlet>
    <servlet-name>MyServlet</servlet-name>
    <servlet-class>org.springframework.web.servlet.DispatcherServlet</servlet-class>
    <init-param>
      <param-name>contextConfigLocation</param-name>
      <param-value></param-value>
    </init-param>
    <load-on-startup>1</load-on-startup>
  </servlet>

  <servlet-mapping>
    <servlet-name>MyServlet</servlet-name>
    <url-pattern>/</url-pattern>
  </servlet-mapping>

  <welcome-file-list>
    <welcome-file></welcome-file>
  </welcome-file-list>

</web-app>
At last we add one @ImportSource line in our WebConfig configuration class:
@EnableWebMvc
@Configuration
@ComponentScan(basePackages = "com.jverstry")
@ImportResource("/WEB-INF/MyServlet-security.xml")
public class WebConfig extends WebMvcConfigurerAdapter {

  @Bean
  public ViewResolver getViewResolver() {

    InternalResourceViewResolver resolver = new InternalResourceViewResolver();
    resolver.setPrefix("WEB-INF/pages/");
    resolver.setSuffix(".jsp");

    return resolver;

  }

}

Running The Example

After compiling the project, one can run it using the maven tomcat:run goal. Then, browse:

  http://localhost:9191/spring-mvc-with-annotations/

Login with guest guest:


 ...and access the main page:


More Spring related posts here.